I’m a
I’m a CS Student, Developer, and Problem Solver.
I build useful things with code, data, and a suspicious amount of curiosity.
Computer Science @ UCalgary — exploring software, machine learning, and whatever interesting problem comes next.
about
I’m Farhan, a Computer Science student at the University of Calgary. I like building things that take a messy problem and turn it into something useful — whether that means analyzing thousands of traffic incidents, working with machine-learning models, or building a small application from scratch. Right now I’m exploring software engineering, data, ML, and cloud technologies. Mostly, I’m interested in understanding how things work and getting better by actually building them.
status: learning, building, occasionally debugging why it worked yesterday.
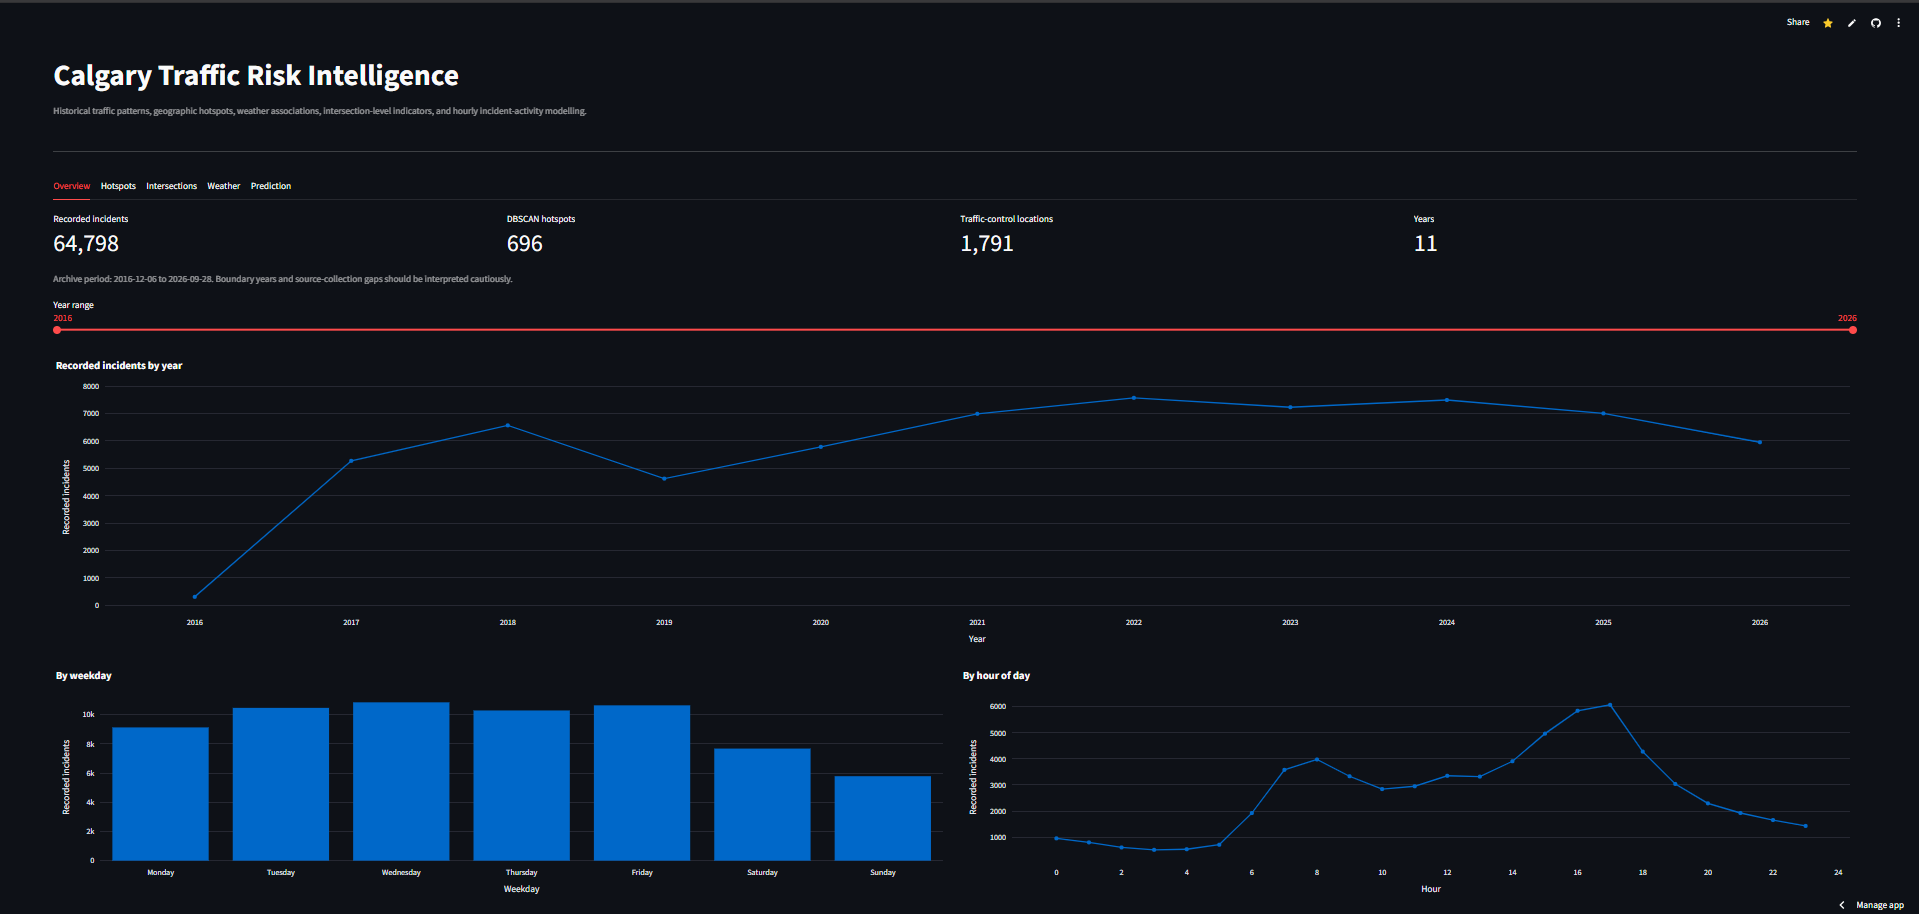
Built an end-to-end traffic analytics and machine learning project using more than 64,000 Calgary traffic incident records. The project combines temporal analysis, DBSCAN-based hotspot detection, nearest traffic-control matching, historical weather data, a custom intersection-level risk index, and an hourly incident-activity prediction model. The results are presented through an interactive Streamlit dashboard with maps, charts, risk insights, and model predictions.
Exploring Student Perceptions and Motivations Behind Campus Gym Usage
2025
Collaborated in a team to analyze University of Calgary students’ campus gym usage, motivations, and barriers. My primary contribution was data cleaning and preparation, including removing irrelevant metadata and incomplete responses, reorganizing survey data into meaningful groups, standardizing numerical coding, and improving the dataset structure for analysis and visualization. The cleaned dataset supported the team’s final statistical analysis and findings.
Excel · Qualtrics · Data Cleaning · Statistical Analysis · Data Visualization
Completed an individual cybersecurity project in a controlled virtual lab, working through a full attack path from network discovery to retrieving a target file. I used tools and techniques including Nmap, service enumeration, web application inspection, Vigenère cipher decryption, SSH, Linux file permissions, steganography, privilege escalation, and SCP. The project strengthened my understanding of how small security weaknesses can combine into larger system vulnerabilities.